FBI Investigates Major Security Breach of National Crime Information Center Database Sparking Officer Safety Concerns

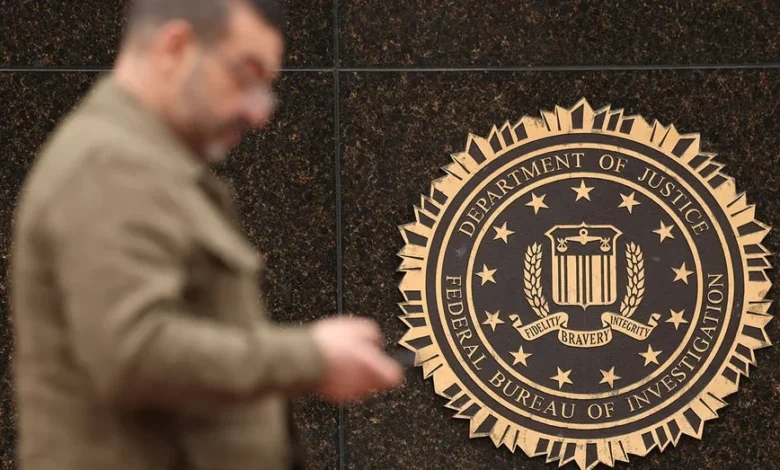
The Federal Bureau of Investigation is facing intense scrutiny and launching a high-priority internal investigation following a major cyber intrusion into the National Crime Information Center (NCIC). According to multiple sources familiar with the matter, hackers successfully breached the critical law enforcement database, marking the second high-profile cyberattack against the bureau in recent months. The breach has alarmed national security experts, law enforcement officials, and federal legislators, largely because the NCIC serves as the digital backbone for everyday police operations across the United States.
The incident has immediately elevated concerns regarding officer safety during routine traffic stops and field encounters. While investigators work around the clock to assess the full scope of the breach, the lack of immediate confirmation regarding data integrity leaves a dangerous margin of error. As federal agencies grapple with an escalating landscape of sophisticated cyberthreats, this latest penetration exposes critical vulnerabilities in federal infrastructure and highlights the growing reliance on digital networks that are increasingly targeted by malicious actors.
The Function and Critical Importance of the NCIC Database
To understand the severity of the breach, one must examine the fundamental role the National Crime Information Center plays in American law enforcement. Established in 1967, the NCIC is often described by cybersecurity and law enforcement veterans as "America’s computer for law enforcement." It is a centralized, real-time electronic database managed by the FBI in conjunction with criminal justice agencies nationwide.
The system operates on an expansive scale. Approximately 56 state and territorial terminals feed continuous streams of information down to hundreds of thousands of mobile data terminals installed in patrol cars across the country. When a police officer pulls a vehicle over, runs a license plate, or checks an individual’s identification, the query travels through local systems directly into the NCIC database.
Within seconds, the system provides vital information regarding active warrants, protection orders, stolen vehicles, missing persons, wanted fugitives, and suspected terrorists. Furthermore, the database houses sensitive personally identifiable information (PII), including names, dates of birth, and Social Security numbers of individuals flagged within the criminal justice system. Although the NCIC does not contain highly classified intelligence or sensitive counterintelligence case files, its day-to-day operational utility is unmatched, making it a uniquely attractive target for bad actors seeking to disrupt public safety or manipulate judicial processes.
Immediate Reactions and Law Enforcement Warnings
The revelation of the breach has triggered swift reactions from retired law enforcement personnel and national leaders. Jason Pack, a retired FBI supervisory special agent who specialized in cybercrime and public information, spoke candidly about the profound risks associated with the intrusion.
"What they worry about is if any of this data has changed, then it might affect officers’ safety on the side of the road," Pack stated during an interview. He emphasized that the primary objective for the FBI’s incident response team is to immediately determine whether internal data was altered, falsified, or scrubbed. Even minor manipulations to warrant records or criminal histories could lead to catastrophic outcomes in the field, either by giving a false sense of security to an officer confronting a dangerous fugitive or by wrongfully detaining an innocent citizen due to corrupted data.
Political leaders have also begun weighing in on the escalating security crisis. President Donald Trump addressed the intrusion during a morning media appearance, stating that he had just been briefed on the cyberattack. "I will say that it’s not good. I don’t like that," the president remarked, reflecting the growing administration-wide frustration over persistent vulnerabilities in federal cybersecurity architecture.
A Timeline of Recent Cyber Incidents Targeting the Bureau
This unauthorized access to the NCIC database is not an isolated event; rather, it represents a troubling escalation in a series of digital sieges against America’s premier law enforcement agency. The timeline of recent cyber intrusions points to a concerted effort by advanced persistent threat groups and financially motivated extortion syndicates to probe, infiltrate, and exploit federal networks.
The sequence of events leading up to the current investigation highlights a rapidly deteriorating security posture:
- September: The notorious extortion and hacking collective known as ShinyHunters successfully breached an external FBI job portal website. The group publicly claimed to have exfiltrated sensitive personal records and employment data belonging to bureau personnel.
- October and November: Federal oversight bodies, including the Government Accountability Office (GAO), published scathing reports detailing widespread non-compliance with federal cybersecurity standards. The GAO found that 17 out of 22 major federal agencies failed to meet basic regulatory requirements to secure their digital infrastructure.
- December: Sources revealed that hackers successfully bypassed security perimeters to breach the National Crime Information Center database, prompting emergency investigations by the FBI’s cyber division and raising urgent alarm bells across state and local police departments.
The Mechanics of Modern Cyberattacks: Machine Speed and AI
The methods employed by modern cybercriminals have evolved far beyond traditional hacking techniques. According to security experts, intrusions are now executed at "machine speed," fueled by artificial intelligence and automated reconnaissance tools that constantly scan federal networks for unpatched vulnerabilities, weak credentials, or configuration errors.

Investigators analyzing the NCIC breach are examining complex metadata and Internet Protocol (IP) logs to trace the entry point of the attackers. Analysts are exploring multiple vectors:
- Compromised Credentials: With more than 100,000 authorized users accessing the system nationwide, attackers may have utilized stolen or phished passwords to gain legitimate-looking access.
- State Terminal Infiltration: Because local and state law enforcement agencies connect to the federal database through regional terminals, a vulnerability in a state-level network could have served as a backdoor into the central repository.
- Third-Party Vendor Exploitation: Supply chain vulnerabilities remain a persistent weak spot, allowing hackers to compromise external contractors who maintain software integrations with law enforcement platforms.
This creates an ongoing, high-stakes dynamic. Cybersecurity professionals are forced to play constant defense, attempting to patch vulnerabilities as fast as automated scripts can find them. The integration of AI into cyberattacks has leveled the playing field for criminal syndicates, enabling them to launch coordinated, multi-vector assaults that outpace traditional human-managed defense systems.
Broader Implications for National Security and Federal Oversight
The breach of the NCIC database extends far beyond technical data loss; it strikes at the heart of public trust in federal institutions. When citizens believe that law enforcement databases are secure, they trust that their personal information is guarded against criminal exploitation. When those systems are repeatedly compromised, confidence in government competence begins to erode.
Furthermore, the timing of this attack aligns with broader systemic concerns regarding federal cybersecurity readiness. The recent findings by the Government Accountability Office—showing that the vast majority of federal agencies fail to meet baseline security compliance—underscore a systemic failure in resource allocation, software modernization, and proactive defense mechanisms. Critics argue that despite billions of dollars allocated annually to federal cybersecurity initiatives, bureaucratic inertia and legacy infrastructure continue to leave critical databases exposed to foreign adversaries and domestic cybercriminals alike.
As the FBI’s incident response teams continue their forensic analysis, the agency has yet to officially confirm the extent of the data compromise or formally attribute the attack to a specific threat actor. However, as the investigation unfolds, the pressure mounts on federal authorities to not only secure the NCIC database against further manipulation but also to restore confidence in an agency tasked with protecting the nation’s most sensitive digital and physical borders.
Related posts: